PCI DSS
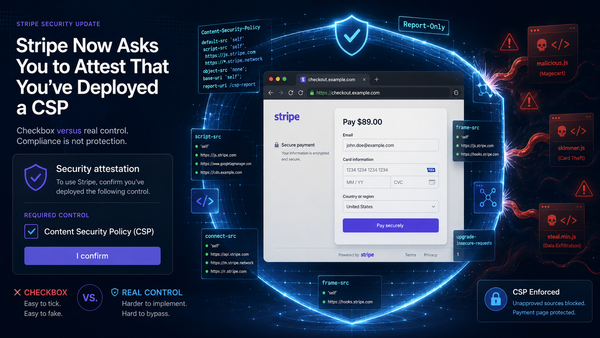
Stripe Now Asks You to Attest That You've Deployed a CSP
Stripe's PCI assessment now has a mandatory checkbox: confirm you've deployed a Content Security Policy. Here's what you're attesting to, and how to do it.
PCI DSS
Stripe's PCI assessment now has a mandatory checkbox: confirm you've deployed a Content Security Policy. Here's what you're attesting to, and how to do it.
Newsletter
June was all about giving you tighter control over who can reach your account and much richer visibility into what happens inside it. Here's everything we shipped. Single Sign-On with SAML 2.0 - Beta 🪪 You can now sign in to Report URI through your own identity provider.
One thing I've learned over the years is that the best businesses don't simply react to change. They position themselves where change is happening. That applies just as much to cybersecurity as it does to any other industry. Every year, organisations invest millions in new security
Newsletter
May has been a busy month at Report URI HQ, with a big push on account security alongside a host of improvements to how we surface threats in your reports. Here's everything we shipped. Device Bound Session Credentials - Beta 🔐 We've implemented the emerging Device Bound Session
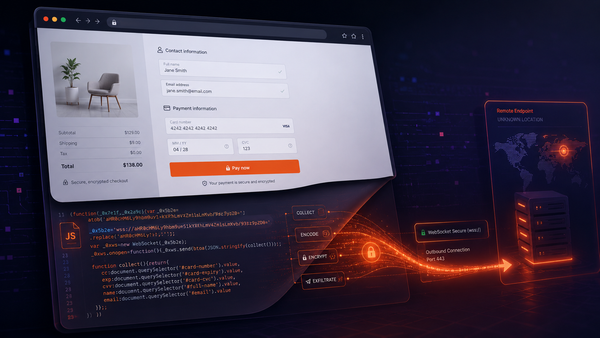
A recent WooCommerce attack, analysed by Scott Helme, Report URI's CEO, exposed something many organisations are still struggling to fully grasp: Your website can be actively stealing customer payment data while appearing to function completely normally. No outage. No ransomware. No obvious breach. No backend compromise alerts. Customers
Newsletter
As we continue to push into 2026, we’ve maintained our pace of improving existing features and introducing new ones. API and MCP endpoints - now Generally Available 🤖 Our API and MCP endpoints are now Generally Available to customers on a suitable plan! The feedback from the beta was amazing and
White Paper
Passkeys are one of the best improvements to online security in a long time. They are designed to replace passwords with a safer, easier way to sign in. That means no more reused passwords, much less risk from phishing emails, and far better protection against attackers trying stolen login details
Newsletter
Both January and February were big months for us at Report URI HQ, and we have continued to push forwards in March! API and MCP endpoints - beta invites! 🤖 Starting out with what has to be our most exciting news, we are announcing that we have started a closed beta for
NCSC
Most organisations don’t have a clear view of their external attack surface, what’s exposed, what’s changed, and where risk may be building over time. For many UK organisations, the National Cyber Security Centre’s Web Check and Mail Check services have quietly filled part of that gap.
Stripe has recently updated its security guidance to explicitly require merchants to have visibility into what code is running on their websites. In their certification process is a clear expectation: organisations handling payments should be monitoring client-side behaviour, not just backend systems. This isn’t a new regulation or
Newsletter
After kicking 2026 off with a pretty big update, we've continued to push forwards with a lot of work across the board at Report URI HQ.
Magecart
In late 2024, extending into 2025, the European Space Agency was forced to take its online store offline following a Magecart-style attack that compromised customer payment data. The incident was not the result of a traditional breach, stolen credentials, or a failure of perimeter security. It happened quietly, inside